

[Mar 19, 2022] Free CheckPoint 156-215.80 Exam Questions and Answer
Verified 156-215.80 dumps Q&As Latest 156-215.80 Download
Certification Path
The Check Point Certified Security Administrator (CCSA R80) 156-215.80 Exam certification path includes only one 156-215.80 certification exam.
NEW QUESTION 81
Vanessa is firewall administrator in her company; her company is using Check Point firewalls on central and remote locations, which are managed centrally by R80 Security Management Server. One central location has an installed R77.30 Gateway on Open server. Remote location is using Check Point UTM-1
570 series appliance with R71. Which encryption is used in Secure Internal Communication (SIC) between central management and firewall on each location?
- A. On central firewall AES128 encryption is used for SIC, on Remote firewall 3DES encryption is used for SIC.
- B. The Firewall Administrator can choose which encryption suite will be used by SIC.
- C. On central firewall AES256 encryption is used for SIC, on Remote firewall AES128 encryption is used for SIC.
- D. On both firewalls, the same encryption is used for SIC. This is AES-GCM-256.
Answer: A
Explanation:
Gateways above R71 use AES128 for SIC. If one of the gateways is R71 or below, the gateways use
3DES.
Reference:
http://dl3.checkpoint.com/paid/74/74d596decb6071a4ee642fbdaae7238f/
CP_R80_SecurityManagement_AdminGuide.pdf?
HashKey=1479584563_6f823c8ea1514609148aa4fec5425db2&xtn=.pdf
NEW QUESTION 82
Which option in a firewall rule would only match and allow traffic to VPN gateways for one Community in
common?
- A. Specific VPN Communities
- B. All Connections (Clear or Encrypted)
- C. Accept all encrypted traffic
- D. All Site-to-Site VPN Communities
Answer: A
NEW QUESTION 83
You work as a security administrator for a large company. CSO of your company has attended a security conference where he has learnt how hackers constantly modify their strategies and techniques to evade detection and reach corporate resources. He wants to make sure that his company has the right protections in place. Check Point has been selected for the security vendor. Which Check Point products protects BEST against malware and zero-day attacks while ensuring quick delivery of safe content to your users?
- A. IPS, anti-virus and anti-bot
- B. SandBlast
- C. IPS and Application Control
- D. IPS, anti-virus and e-mail security
Answer: B
Explanation:
SandBlast Zero-Day Protection
Hackers constantly modify their strategies and techniques to evade detection and reach corporate resources.
Zero-day exploit protection from Check Point provides a deeper level of inspection so you can prevent more malware and zero-day attacks, while ensuring quick delivery of safe content to your users.
Reference: https://www.checkpoint.com/products-solutions/zero-day-protection/
NEW QUESTION 84
Where is the "Hit Count" feature enabled or disabled in SmartConsole?
- A. In Global Properties for the Security Management Server
- B. On each Security Gateway
- C. On the Policy layer
- D. On the Policy Package
Answer: B
NEW QUESTION 85
Which Check Point software blade prevents malicious files from entering a network using virus signatures and anomaly-based protections from ThreatCloud?
- A. Application Control
- B. Firewall
- C. Anti-spam and Email Security
- D. Antivirus
Answer: D
Explanation:
The enhanced Check Point Antivirus Software Blade uses real-time virus signatures and anomaly-based protections from ThreatCloud, the first collaborative network to fight cybercrime, to detect and block malware at the gateway before users are affected.
Reference: https://www.checkpoint.com/products/antivirus-software-blade/
NEW QUESTION 86
What will be the effect of running the following command on the Security Management Server?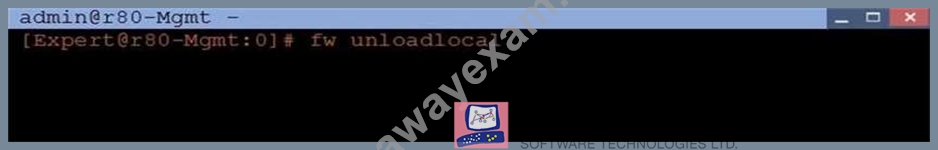
- A. Remove the installed Security Policy.
- B. Reset SIC on all gateways.
- C. Remove the local ACL lists.
- D. No effect.
Answer: A
Explanation:
This command uninstall actual security policy (already installed)
Reference: https://sc1.checkpoint.com/documents/R77/
CP_R77_SecurityGatewayTech_WebAdmin/6751.htm
NEW QUESTION 87
Choose what BEST describes a Session.
- A. Starts when an Administrator publishes all the changes made on SmartConsole.
- B. Sessions ends when policy is pushed to the Security Gateway.
- C. Sessions locks the policy package for editing.
- D. Starts when an Administrator logs in to the Security Management Server through SmartConsole and ends when it is published.
Answer: D
Explanation:
Explanation/Reference:
Explanation:
Administrator Collaboration
More than one administrator can connect to the Security Management Server at the same time. Every administrator has their own username, and works in a session that is independent of the other administrators.
When an administrator logs in to the Security Management Server through SmartConsole, a new editing session starts. The changes that the administrator makes during the session are only available to that administrator. Other administrators see a lock icon on object and rules that are being edited.
To make changes available to all administrators, and to unlock the objects and rules that are being edited, the administrator must publish the session.
Reference: https://sc1.checkpoint.com/documents/R80/CP_R80_SecMGMT/html_frameset.htm?
topic=documents/R80/CP_R80_SecMGMT/117948
NEW QUESTION 88
What are the three essential components of the Check Point Security Management Architecture?
- A. SmartConsole, Security Management Server, Security Gateway
- B. WebUI, SmartConsole, Security Gateway
- C. SmartConsole, SmartUpdate, Security Gateway
- D. Security Management Server, Security Gateway, Command Line Interface
Answer: A
Explanation:
Deployments
Basic deployments: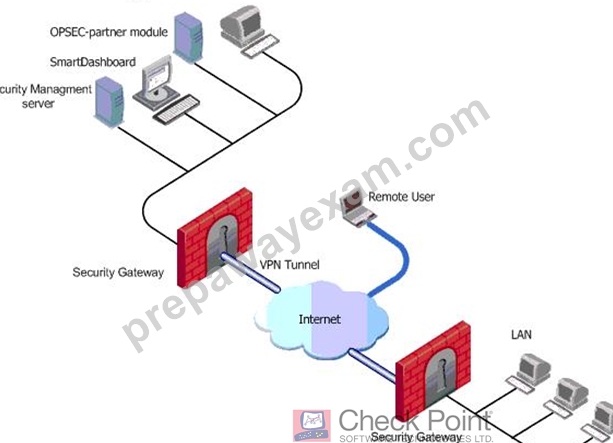
Assume an environment with gateways on different sites. Each Security Gateway connects to the Internet on one side, and to a LAN on the other.
You can create a Virtual Private Network (VPN) between the two Security Gateways, to secure all communication between them.
The Security Management server is installed in the LAN, and is protected by a Security Gateway. The Security Management server manages the Security Gateways and lets remote users connect securely to the corporate network. SmartDashboard can be installed on the Security Management server or another computer.
There can be other OPSEC-partner modules (for example, an Anti-Virus Server) to complete the network security with the Security Management server and its Security Gateways.
NEW QUESTION 89
Customer's R80 management server needs to be upgraded to R80.10. What is the best upgrade method when
the management server is not connected to the Internet?
- A. Export R80 configuration, clean install R80.10 and import the configuration
- B. CPUSE offline upgrade
- C. SmartUpdate upgrade
- D. CPUSE online upgrade
Answer: B
NEW QUESTION 90
Two administrators Dave and Jon both manage R80 Management as administrators for ABC Corp. Jon logged into the R80 Management and then shortly after Dave logged in to the same server. They are both in the Security Policies view. From the screenshots below, why does Dave not have the rule no.6 in his SmartConsole view even though Jon has it his in his SmartConsole view?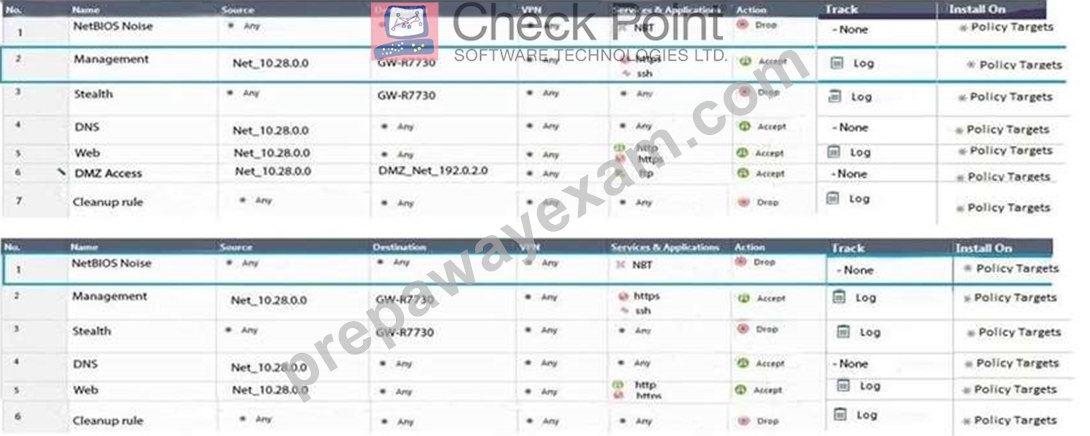
- A. Jon is currently editing rule no.6 but has not yet Published his changes.
- B. Dave is currently editing rule no.6 and has marked this rule for deletion.
- C. Jon is currently editing rule no.6 but has Published part of his changes.
- D. Dave is currently editing rule no.6 and has deleted it from his Rule Base.
Answer: A
Explanation:
When an administrator logs in to the Security Management Server through SmartConsole, a new editing session starts. The changes that the administrator makes during the session are only available to that administrator. Other administrators see a lock icon on object and rules that are being edited. To make changes available to all administrators, and to unlock the objects and rules that are being edited, the administrator must publish the session.
Reference:
http://dl3.checkpoint.com/paid/74/74d596decb6071a4ee642fbdaae7238f/
CP_R80_SecurityManagement_AdminGuide.pdf?
HashKey=1479584563_6f823c8ea1514609148aa4fec5425db2&xtn=.pdf
NEW QUESTION 91
Which of the following is considered to be the more secure and preferred VPN authentication method?
- A. Password
- B. MD5
- C. Certificate
- D. Pre-shared secret
Answer: C
NEW QUESTION 92
Each cluster has __________ interfaces.
- A. Two
- B. Four
- C. Five
- D. Three
Answer: D
Explanation:
Explanation
Each cluster member has three interfaces: one external interface, one internal interface, and one for synchronization. Cluster member interfaces facing in each direction are connected via a switch, router, or VLAN switch.
NEW QUESTION 93
The IT Management team is interested in the new features of the Check Point R80 Management and wants to
upgrade but they are concerned that the existing R77.30 Gaia Gateways cannot be managed by R80 because it
is so different. As the administrator responsible for the Firewalls, how can you answer or confirm these
concerns?
- A. R80 Management was designed as a completely different Management system and so can only monitor
Check Point Gateways prior to R80. - B. R80 Management cannot manage earlier versions of Check Point Gateways prior to R80. Only R80 and
above Gateways can be managed. Consult the R80 Release Notes for more information. - C. R80 Management requires the separate installation of compatibility hotfix packages for managing the
earlier versions of Check Point Gateways prior to R80. Consult the R80 Release Notes for more
information. - D. R80 Management contains compatibility packages for managing earlier versions of Check Point
Gateways prior to R80. Consult the R80 Release Notes for more information.
Answer: D
Explanation:
Explanation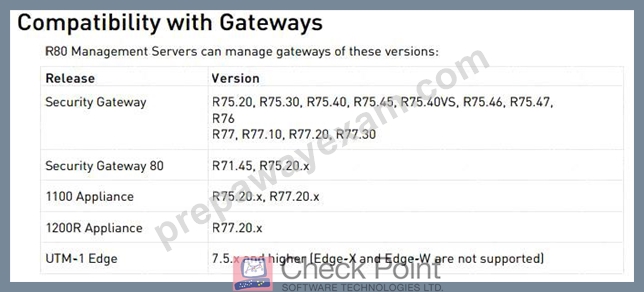
NEW QUESTION 94
Fill in the blanks: VPN gateways authenticate using ___________ and ___________ .
- A. Passwords; tokens
- B. Tokens; pre-shared secrets
- C. Certificates; passwords
- D. Certificates; pre-shared secrets
Answer: D
Explanation:
Explanation
VPN gateways authenticate using Digital Certificates and Pre-shared secrets.
References:
NEW QUESTION 95
Which of the following authentication methods can be configured in the Identity Awareness setup wizard?
- A. Windows password
- B. TACACS
- C. Check Point Password
- D. LDAP
Answer: D
Explanation:
Explanation
NEW QUESTION 96
View the rule below. What does the lock-symbol in the left column mean? Select the BEST answer.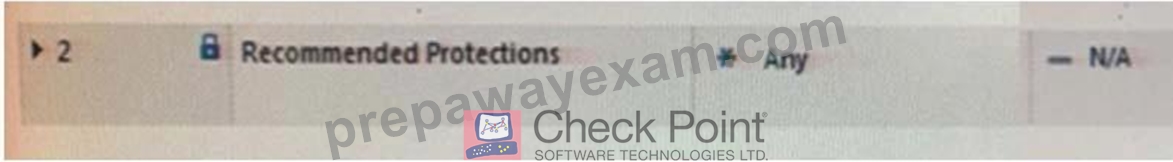
- A. The current administrator has read-only permissions to Threat Prevention Policy.
- B. Another user has locked the rule for editing.
- C. The current administrator is logged in as read-only because someone else is editing the policy.
- D. Configuration lock is present. Click the lock symbol to gain read-write access.
Answer: B
Explanation:
Explanation/Reference:
Explanation: Administrator Collaboration
More than one administrator can connect to the Security Management Server at the same time. Every administrator has their own username, and works in a session that is independent of the other administrators.
When an administrator logs in to the Security Management Server through SmartConsole, a new editing session starts. The changes that the administrator makes during the session are only available to that administrator. Other administrators see a lock icon on object and rules that are being edited.
To make changes available to all administrators, and to unlock the objects and rules that are being edited, the administrator must publish the session.
Reference: https://sc1.checkpoint.com/documents/R80/CP_R80_SecMGMT/html_frameset.htm?
topic=documents/R80/CP_R80_SecMGMT/124265
NEW QUESTION 97
What are the two types of address translation rules?
- A. Untranslated packet and manipulated packet
- B. Manipulated packet and original packet
- C. Original packet and translated packet
- D. Translated packet and untranslated packet
Answer: C
Explanation:
NAT Rule Base
The NAT Rule Base has two sections that specify how the IP addresses are translated:
NEW QUESTION 98
You have just installed your Gateway and want to analyze the packet size distribution of your traffic with SmartView Monitor.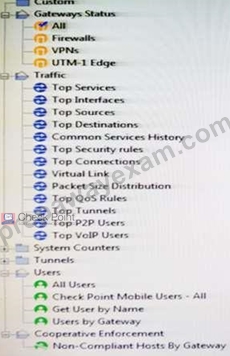
Unfortunately, you get the message:
"There are no machines that contain Firewall Blade and SmartView Monitor".
What should you do to analyze the packet size distribution of your traffic? Give the BEST answer.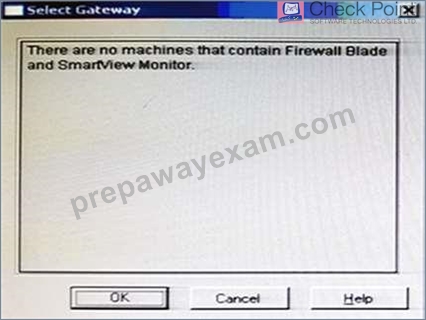
- A. Purchase the SmartView Monitor license for your Security Management Server.
- B. Enable Monitoring on your Security Gateway.
- C. Purchase the SmartView Monitor license for your Security Gateway.
- D. Enable Monitoring on your Security Management Server.
Answer: B
NEW QUESTION 99
......
Use Real Dumps - 100% Free 156-215.80 Exam Dumps: https://www.prepawayexam.com/CheckPoint/braindumps.156-215.80.ete.file.html